Meet Our Customer
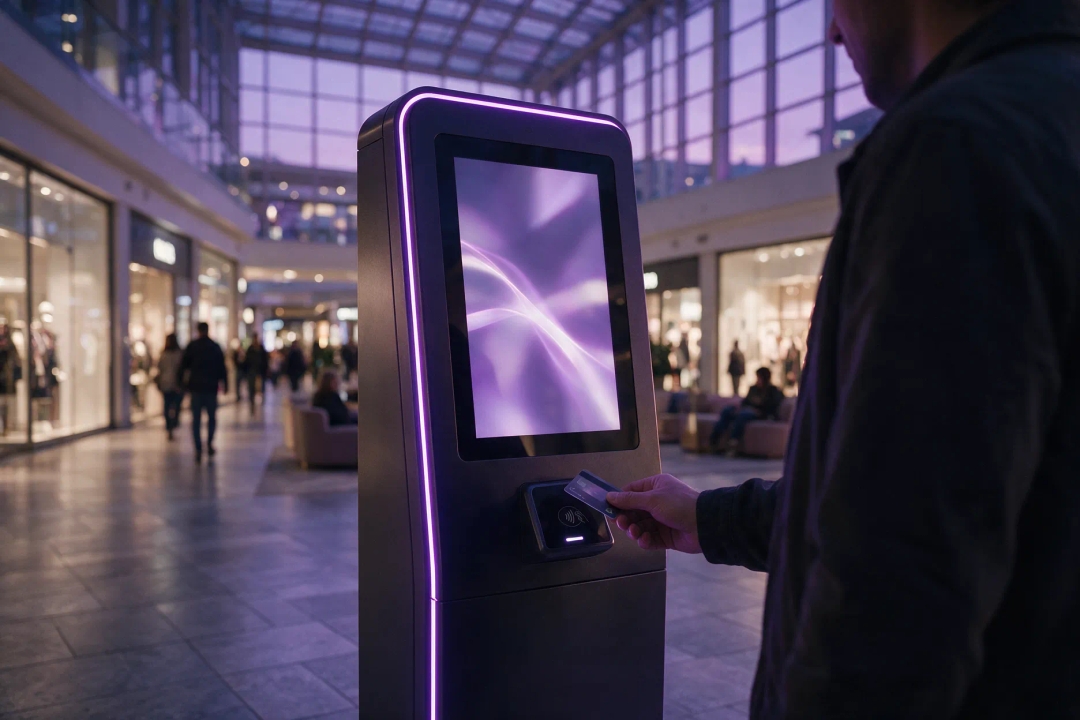
Kiosk is a digital payments platform designed to support secure and accessible transaction services through a distributed kiosk channel. The service connects customer-facing kiosks with payment applications, database platforms, security controls and on-premises systems used for transaction processing and cryptographic services.
The AWS platform must provide reliable availability, protected connectivity, recoverable data services and clear operational accountability, while remaining current as Kubernetes, operating systems, databases, network security components and AWS services evolve.
Challenge
The Kiosk environment spans multiple AWS accounts, hybrid connectivity, container workloads, database platforms and perimeter security components. The customer required more than reactive support: a managed operating model capable of maintaining the platform continuously, coordinating specialist teams and providing evidence for operational and regulatory governance.
- Round-the-clock readiness for production transaction services and UAT.
- Specialist support across EKS, EC2, Aurora PostgreSQL, SQL Server Always On, FortiGate, Transit Gateway and VPN.
- Supported and secure versions across operating systems, Kubernetes, databases, firewalls and infrastructure-as-code dependencies.
- Clear ownership among customer L1, stc Bahrain L2/L3, AWS and the application vendor.
- Reliable backup, restoration, monitoring, evidence and controlled change.
Vision
A continuously maintained, governed AWS platform that keeps payment services available and audit-ready as the underlying technology stack evolves.
Implication
Loss of EKS, databases, firewall or hybrid connectivity could prevent or degrade payments. Unresolved security findings or outdated components could weaken assurance in a regulated environment, unverified backups and runbooks could extend disruption, untested changes could create configuration drift, and ambiguous responsibility could delay diagnosis and restoration.
Solution
stc Bahrain established a managed-services model covering the Kiosk AWS infrastructure and platform layers. The service combines critical-incident coverage with L2/L3 engineering, proactive maintenance, security operations, recovery assurance, infrastructure-as-code governance and recurring reporting.
The environment uses dedicated management, security, log archive, network, production, UAT and shared-services accounts. Production and UAT are governed through central network and security controls, while the workload platform combines Amazon EKS, Amazon EC2, Amazon Aurora PostgreSQL, Microsoft SQL Server Always On, load balancing, centralised observability and hybrid connectivity.
AWS Services
- Governance: AWS Organizations, landing-zone controls, SCPs, IAM Identity Center
- Networking: Amazon VPC, AWS Transit Gateway, Site-to-Site VPN, NAT Gateway, Amazon Route 53, VPC endpoints
- Containers: Amazon EKS, managed node groups, AWS Load Balancer Controller, Kubernetes RBAC
- Compute and data: Amazon EC2, Amazon EBS, Aurora PostgreSQL, SQL Server Always On
- Protection: AWS Backup, Amazon S3 lifecycle, snapshots and point-in-time recovery
- Monitoring: Amazon CloudWatch, CloudWatch Logs, AWS CloudTrail, VPC Flow Logs
- Security: Amazon GuardDuty, AWS Config, AWS KMS, AWS Secrets Manager, security groups and NACLs
- Operations: AWS Systems Manager Patch Manager, OpenTofu / Terraform, ITSM integration
Development
A thirty-day transition covered discovery, access, tooling integration, shadow and reverse-shadow phases, validation of the multi-account environment, L1 runbook creation for health checks, backups, alarms, restarts, escalation and diagnostics, and a formal go-live readiness review before service commencement.
In steady state, the customer retains L1 user contact and initial triage while stc Bahrain provides L2/L3 diagnosis, remediation and permanent corrective action across AWS, network, firewall, EKS, OS, database and storage layers, coordinating with AWS Support and the product vendor. A rolling lifecycle calendar governs the platform:
- Operating systems: monthly Systems Manager patching and approved emergency remediation.
- Amazon EKS: control-plane, node-group and add-on upgrades within AWS support windows.
- Aurora PostgreSQL: version management with UAT rehearsal, cutover and rollback.
- SQL Server Always On: rolling cumulative updates with controlled failover.
- FortiGate: HA-aware firmware upgrades and policy validation.
- Infrastructure as code: provider and module currency, plan validation and drift remediation.
Governance and Reporting
- Weekly operational check-in on incidents, changes, maintenance, risks and SLA status.
- Monthly service review covering SLA, trends, RCA, patching, findings, backup, capacity and drift.
- Quarterly governance board on service trend, Well-Architected findings and improvement roadmap.
- Annual executive review covering performance, roadmap, re-baselining and renewal.
Results
- Improved readiness: named L2/L3 ownership, critical coverage and L1 runbooks support coordinated response.
- Lower lifecycle risk: structured patching keeps platform components supported and secure.
- Stronger assurance: findings triage, access governance, logging and audit support improve visibility.
- Recovery confidence: backup monitoring, restoration testing and maintained runbooks improve recoverability.
- Controlled change: UAT testing, approvals, rollback and code reconciliation reduce drift.
- Continual improvement: performance, posture and Well-Architected reviews drive a prioritised backlog.